Writing
Ship it without shipping the holes.
Practical security for the stack you actually build on. What the defaults get wrong, and how to check your own app before someone else does.
The security checklist nobody runs on a vibecoded app
Seven checks that catch most of what gets skipped when an app is built in a weekend, in the order an attacker would try them.
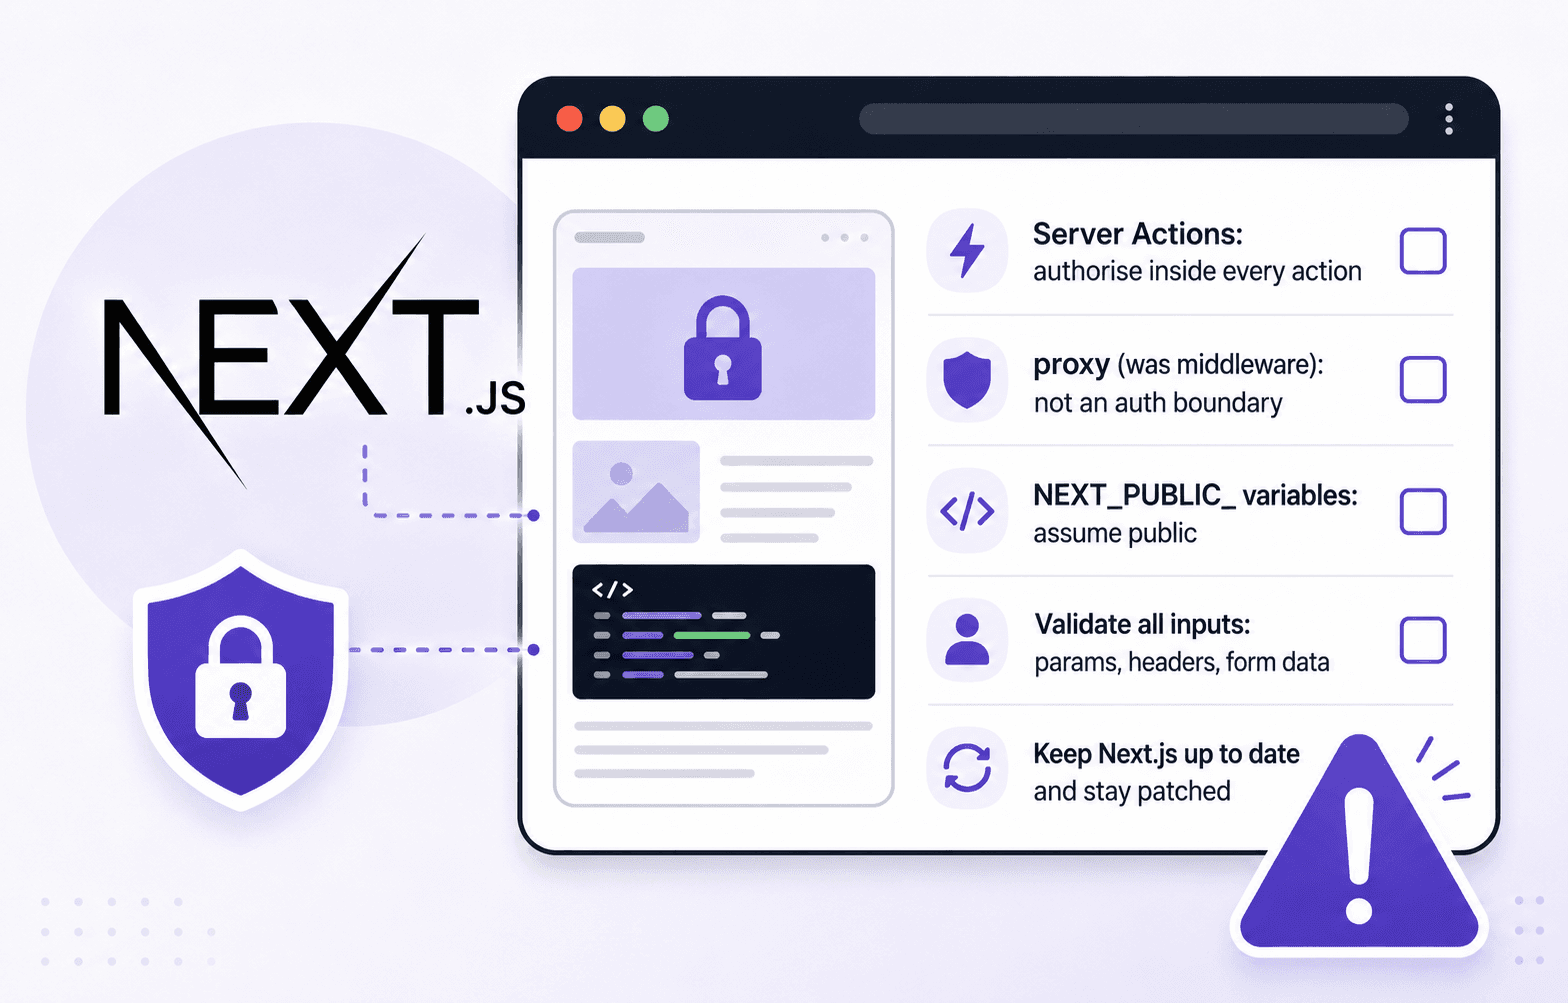
Read the articleA Next.js security checklist that fits on one page
Server Actions, the renamed proxy file, and public environment variables each have a default that surprises people. What to verify before you launch.
Your API key is in your JavaScript bundle
Anything the browser can read, an attacker can read. How to find what you have already shipped, and what to do in the right order once you have.
Four Supabase RLS mistakes that expose every row
Row Level Security is opt-in per table, and the first policies people write usually allow more than they appear to. Four failures, with the fix for each.
Run all of this against your own app.
GhostRecon does the checks in these articles automatically, across your whole attack surface. Free, bring your own model key, runs on your machine.